Limit Login Attempts Security – Login Security, 2FA, Firewall, Brute Force Prevention icon

Limit Login Attempts Security – Login Security, 2FA, Firewall, Brute Force Prevention

Protects WordPress logins against brute force attacks using two-factor authentication, firewall rules, and IP or country-based restrictions. Active on over 1 million sites with a 99.1 PF Score and 4.9/5 user rating.

Generated on 7 Jul 2026. Score and stats mentioned may differ from current live data.

  • #18 Global Rank
  • 1.0M+ active installs
  • 4.8/5 1,483 ratings
  • Mixed support 21 threads
  • Since 2016 10 years active

PF Score (About PF Scores)

PF Score is not a quality guarantee. It is a ranking based on available public signals.

Platinum98.2
Platinum
Gold
Silver
Bronze
Low

Score Breakdown

100
Popularity 40% 1.0M+ active installs
95.5
Reputation 35% 4.8★ from 1,483 ratings
99.1
Freshness 25% Updated 9 days ago

No active penalty: 4 historical CVEs, resolved - details

Download Trends

Loading download data...

Vulnerabilities

4 Total
4 Patched
0 Active
100% Resolved rate
CWE-79 · Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')

The Limit Login Attempts Reloaded plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the plugin's shortcode(s) in all versions up to, and including, 2.25.26 due to insufficient input sanitization and output escaping on user supplied attributes. This makes it possible for authenticated attackers with contributor-level and above permissions to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.

6.4 Medium Affected All - 2.25.26 Patched in ✓ 2.25.27 Published 20 Dec 2023 CVE CVE-2023-6934
CWE-862 · Missing Authorization

The Limit Login Attempts Reloaded plugin for WordPress is vulnerable to unauthorized modification of data due to a missing capability check on the toggle_auto_update() function hooked via AJAX in all versions up to, and including, 2.25.25. This makes it possible for authenticated attackers, with access to a valid nonce, to toggle auto-updates for the plugin on and off.

4.3 Medium Affected All - 2.25.25 Patched in ✓ 2.25.26 Published 6 Nov 2023 CVE CVE-2023-5525
CWE-307 · Improper Restriction of Excessive Authentication Attempts

LimitLoginAttempts.php in the limit-login-attempts-reloaded plugin before 2.17.4 for WordPress allows a bypass of (per IP address) rate limits because the X-Forwarded-For header can be forged. When the plugin is configured to accept an arbitrary header for the client source IP address, a malicious user is not limited to perform a brute force attack, because the client IP header accepts any arbitrary string. When randomizing the header input, the login count does not ever reach the maximum allowed retries.

7.3 High Affected All - 2.17.3 Patched in ✓ 2.17.4 Published 14 Dec 2020 CVE CVE-2020-35590
CWE-79 · Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')

The limit-login-attempts-reloaded plugin before 2.17.4 for WordPress allows wp-admin/options-general.php?page=limit-login-attempts&tab= XSS. A malicious user can cause an administrator user to supply dangerous content to the vulnerable page, which is then reflected back to the user and executed by the web browser. The most common mechanism for delivering malicious content is to include it as a parameter in a URL that is posted publicly or e-mailed directly to victims.

6.1 Medium Affected All - 2.15.2 Patched in ✓ 2.17.4 Published 14 Dec 2020 CVE CVE-2020-35589

Vulnerability data provided by Wordfence Intelligence (opens in a new tab). CVE data: Copyright 1999-2026 The MITRE Corporation. CVE Terms of Use (opens in a new tab).

Support Statistics

21 Support threads
12 Resolved
57% Resolution rate

About Limit Login Attempts Security

WordPress login security with brute force protection, Two-factor authentication (2FA/MFA), firewall, IP/country blocking, and login monitoring

Protect your WordPress website against brute force attacks, bot attacks, and unauthorized login attempts with one of the most trusted login security plugins for WordPress.

Limit Login Attempts Security strengthens your WordPress login security by limiting failed login attempts, blocking malicious IPs, securing wp-login.php, protecting XML-RPC, and adding powerful firewall and 2FA protection without slowing down your website.

Trusted by 2 million WordPress websites, Limit Login Attempts Security is designed specifically to protect the most targeted part of your website: the login page.

Why Use Limit Login Attempts Security?

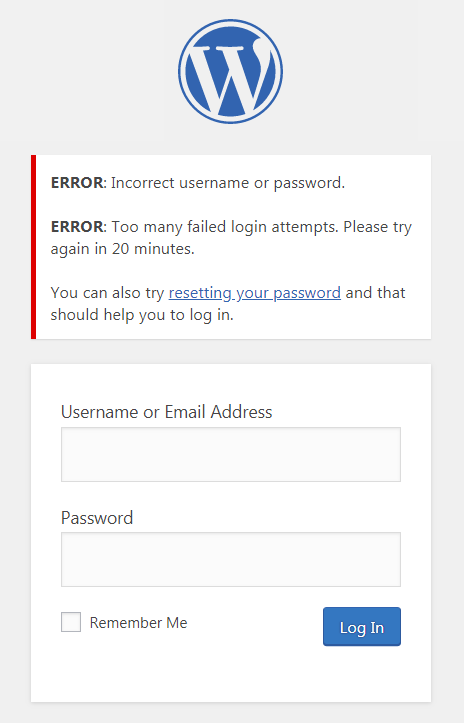
By default, WordPress allows unlimited login attempts. This creates a major security vulnerability where bots and attackers can repeatedly guess usernames and passwords until they gain access. This is especially important in the age of AI, where attackers now have access to faster and more sophisticated tools than ever before.

Limit Login Attempts Security helps stop:

  • Brute force attacks
  • Bot login attacks
  • Credential stuffing attacks
  • XML-RPC attacks
  • Unauthorized login attempts
  • WooCommerce login abuse
  • Malicious IP access attempts

The plugin automatically blocks excessive login attempts and locks out suspicious IP addresses and usernames before attackers can gain access.

Features Included in the Free Version

Login Security & Brute Force Protection

  • Limit login attempts by IP address and username
  • Automatically lock out suspicious login activity
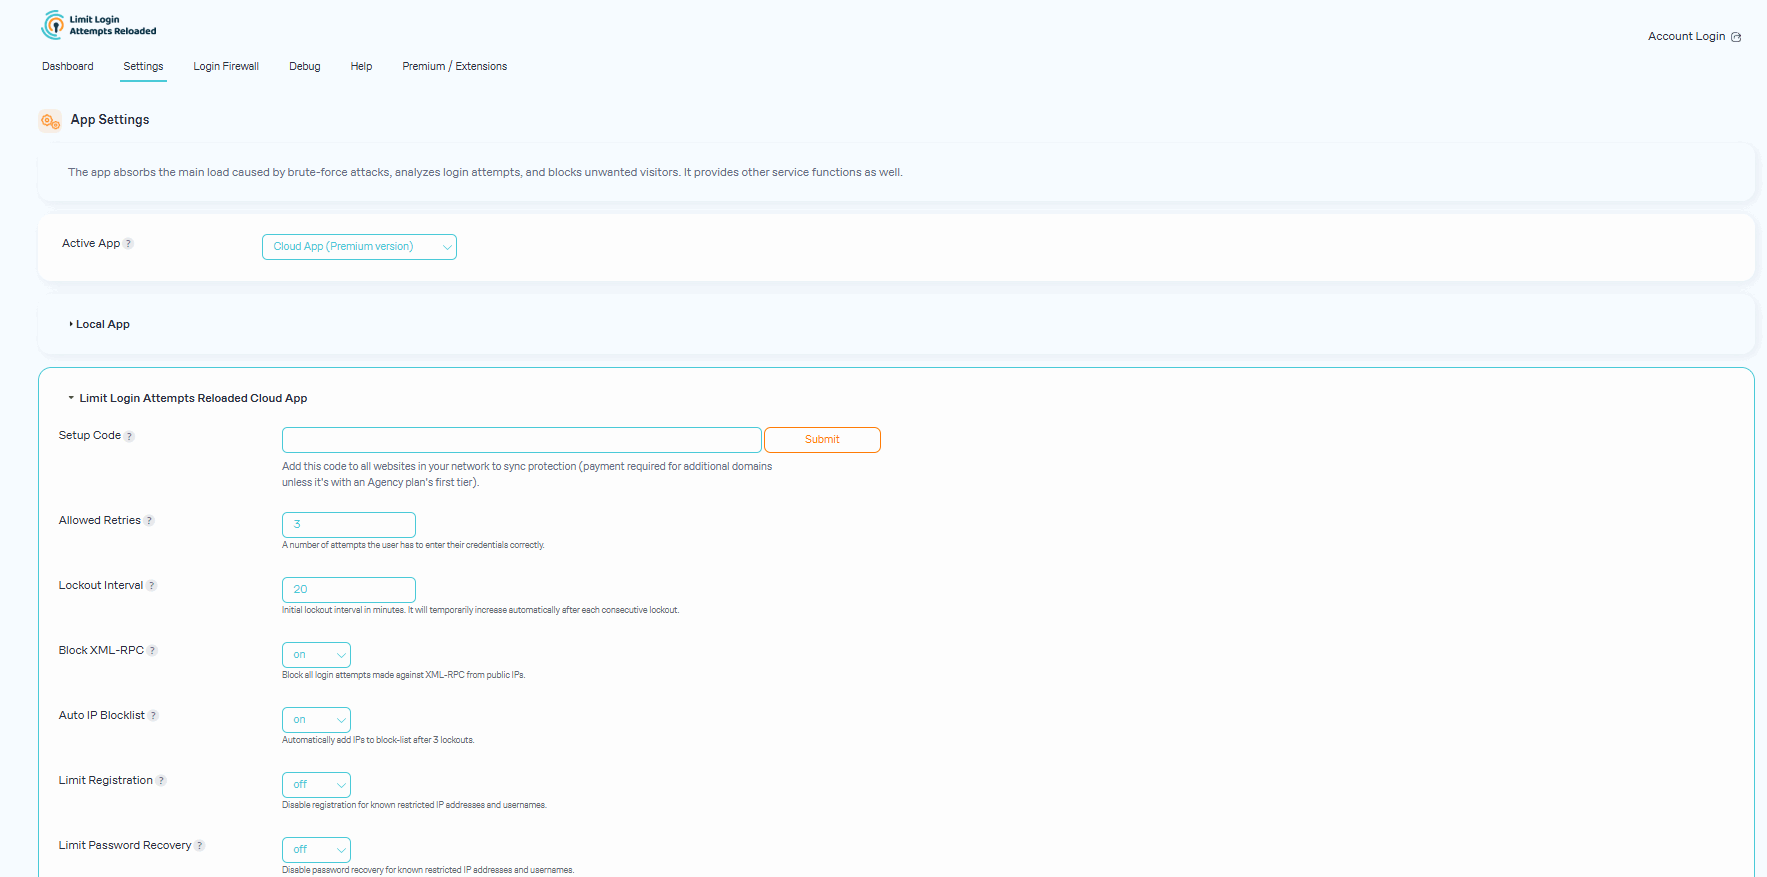
  • Adjustable lockout duration and retry limits
  • Protect wp-login.php from automated attacks
  • Prevent brute force login attacks

2FA / Multi-Factor Authentication (MFA)

  • Built-in two-factor authentication (2FA)
  • Add an additional layer of login protection
  • Improve WordPress account security
  • Secure administrator and user logins

Firewall & Bot Protection

  • Block malicious login requests
  • Detect suspicious login behavior
  • Reduce bot-based login attacks
  • Lightweight firewall-focused login protection

WooCommerce & Plugin Compatibility

Protects:

  • WooCommerce login pages
  • XML-RPC login requests
  • Custom login pages
  • WordPress multisite installations

Compatible With:

  • Wordfence
  • Sucuri
  • Ultimate Member
  • MemberPress
  • WPS Hide Login
  • Cloudflare and reverse proxy setups

Login Monitoring & Notifications

  • Failed login attempt logs
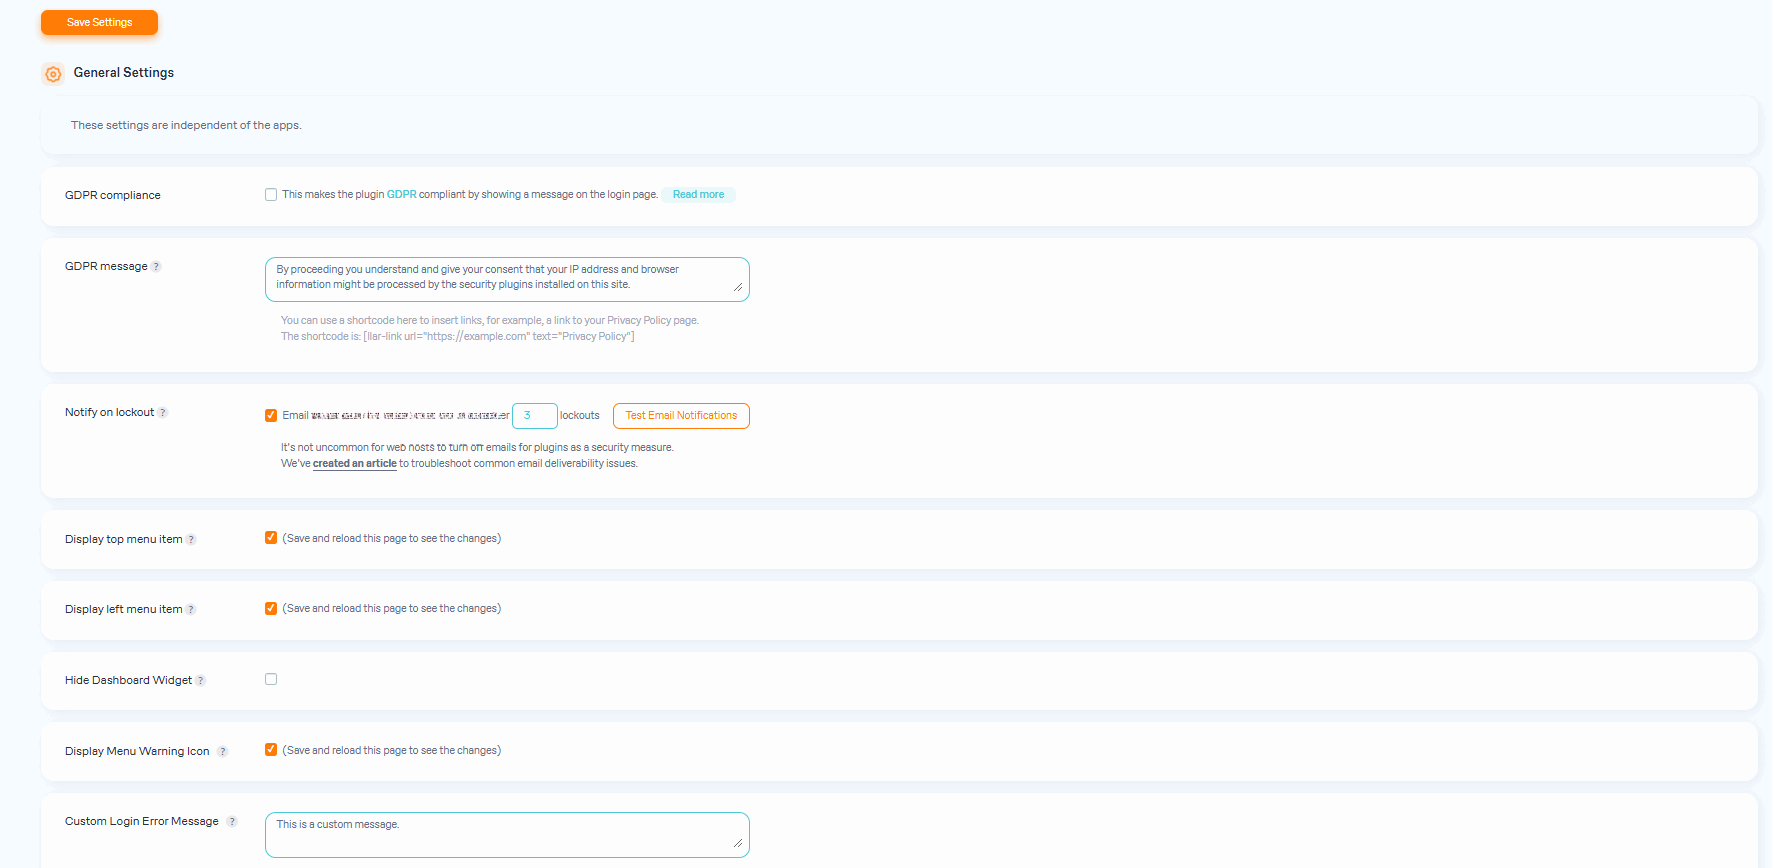
  • Lockout email notifications
  • Denied attempt tracking
  • Login retry visibility for users

Access Controls

  • IP safelist and denylist support
  • Username safelist and denylist support
  • IPv6 range support
  • Custom IP origin configuration

Premium Features (Start Your Free 14 Day Trial)

Upgrade to Limit Login Attempts Security Premium to extend protection with cloud-based login security and advanced attack prevention.

Advanced Cloud Protection

  • Real-time malicious IP intelligence
  • Global denylist protection
  • Synchronized lockouts across websites
  • Auto IP denylist generation
  • Cloud-based login attack mitigation

Enhanced Performance Protection

  • Offload excessive failed login requests from your server
  • Reduce server strain during attacks
  • Improve stability under heavy attack conditions

Advanced Security Features

  • Country-based login blocking
  • Enhanced throttling and lockout escalation
  • Registration page protection
  • Successful login tracking
  • Enhanced lockout analytics and geolocation data

Multi-Site & Team Features

  • Shared safelist and denylist syncing
  • Shared lockout protection between domains
  • Cloud backups of IP security data
  • CSV exports of login and IP activity

Premium Support

  • Access to security-focused support specialists
  • Faster troubleshooting and assistance

Lightweight Security Built for WordPress

Unlike many large security suites, Limit Login Attempts Security focuses specifically on login security and brute force protection.

This means:

  • Faster performance
  • Less server overhead
  • Easier configuration
  • Strong protection without unnecessary bloat

Protect More Than Just wp-login.php

Limit Login Attempts Security secures:

  • wp-login.php
  • XML-RPC
  • WooCommerce logins
  • Custom login forms
  • Registration pages
  • Multisite logins

Trusted by Millions of WordPress Websites

Limit Login Attempts Security is one of the most widely used WordPress login security plugins and has helped protect millions of websites from brute force attacks and malicious login activity.

Whether you run:

  • A personal blog
  • WooCommerce store
  • Membership website
  • Agency
  • Business website
  • Enterprise WordPress network

Limit Login Attempts Security helps secure your login experience with modern WordPress login protection.

Upgrading from the Original Limit Login Attempts Plugin?

Switching is easy:

  1. Remove the old Limit Login Attempts plugin
  2. Install Limit Login Attempts Security
  3. Your settings will remain intact

Translation Support

Currently translated into multiple languages including:

  • Spanish
  • French
  • German
  • Dutch
  • Turkish
  • Swedish
  • Russian
  • Romanian
  • Chinese (Traditional)
  • Brazilian Portuguese
  • And more

Secure Your WordPress Login Today

Install Limit Login Attempts Security and protect your WordPress website with:

  • Login security
  • Two-Factor Authentication (2FA)
  • Brute force protection
  • Firewall security
  • Bot protection
  • XML-RPC protection
  • WooCommerce login protection

Without slowing down your website.
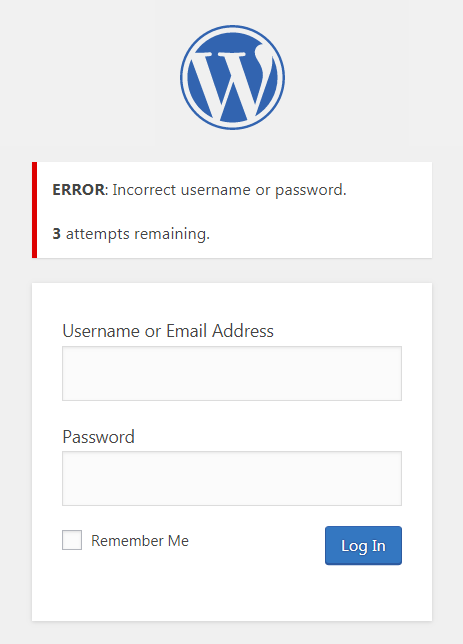
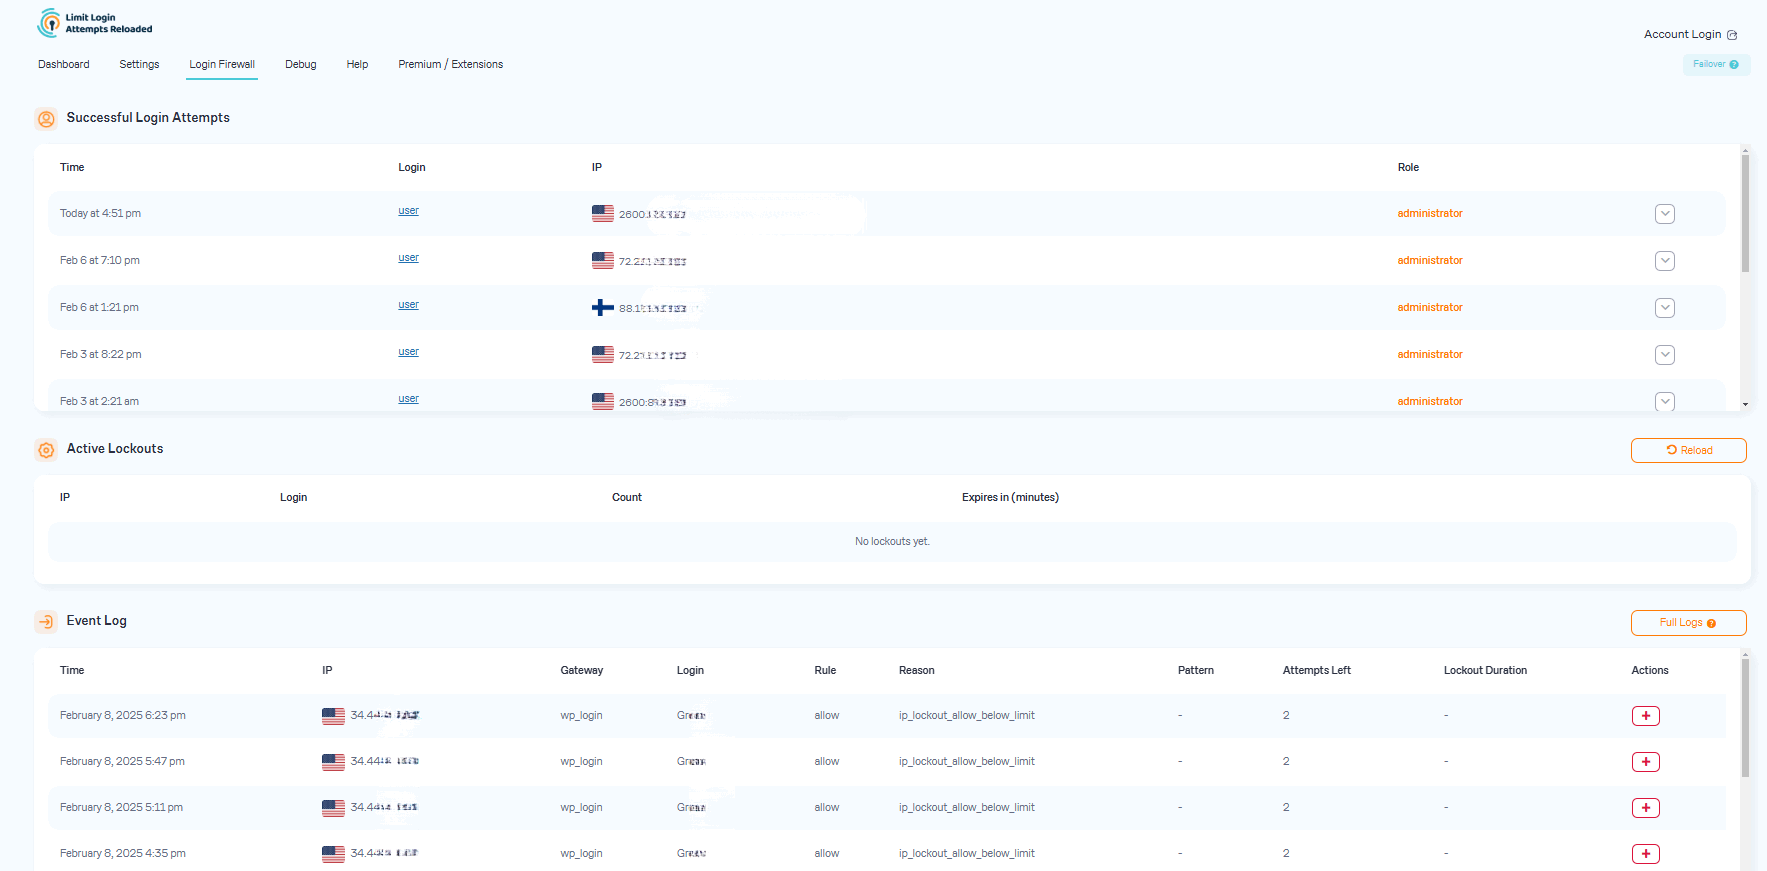
Screenshots

Frequently Asked Questions

What do I do if all users get blocked?

If you are using contemporary hosting, it’s likely your site uses a proxy domain service like CloudFlare, Sucuri, Nginx, etc. They replace your user’s IP address with their own. If the server where your site runs is not configured properly (this happens a lot) all users will get the same IP address. This also applies to bots and hackers. Therefore, locking one user will lead to locking everybody else out. If the plugin is not using our Cloud App, this can be adjusted using the Trusted IP Origin setting. The cloud service intelligently recognizes the non-standard IP origins and handles them correctly, even if your hosting provider does not.

How do I know if I’m under attack?

An easy way to check if the attack is legitimate is to copy the IP address from the lockout notification and check its location using a IP locator tool. If the location is not somewhere you recognize and you have received several failed login attempts, then you are likely being attacked. You might notice dozens or hundreds of IPs each day. Visit our website to learn how can you prevent brute force attacks on your website.

How can I tell that the premium plugin is working?

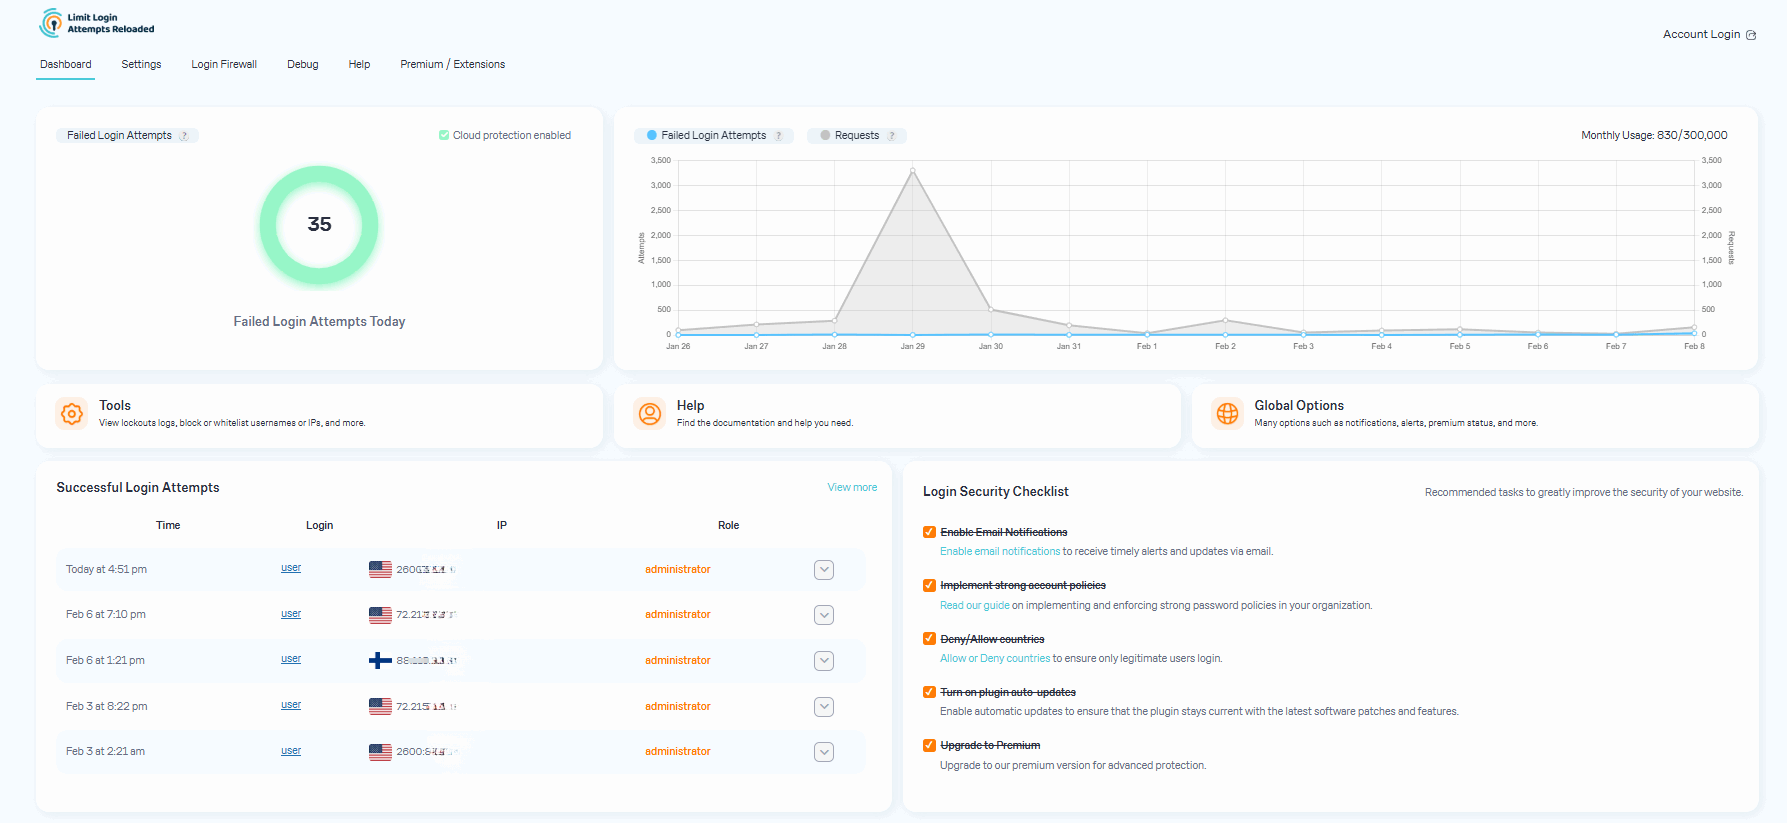
After you upgrade to our premium version, you will see a new dashboard in your WordPress admin that shows all attacks that will now relay through our cloud service. On the graph, you’ll see requests and failed login attempts. Each request will represent the cloud app validating an IP, which also includes denied logins.

In some cases, you may notice an increase in speed and efficiency with your website. Also, a reduction in lockout notifications via email.

Could these failed login attempts be fake?

Some users find it hard to believe that they could experience numerous unsuccessful login attempts, particularly when their site has just been established or has minimal human traffic. The plugin is not responsible for generating these failed login attempts. Newly created websites are frequently hosted on shared IP addresses, making it easy for hackers to discover them. Additionally, newly registered domain names are often crawled soon after creation, rendering a WordPress website susceptible to attacks. Such websites are attractive targets as security is not a primary concern for their owners. We’ve created an article that delves deeper into the issue of fake login attempts in WordPress.

What happens if my site exceeds the request limits in the plan?

The premium plan’s resource limits start from 100,000 requests per month, which should accept almost any heavy brute-force attack. We monitor all of our sites and will alert the user if it appears they are going over their limits. If limits are reached, we will suggest to the user upgrading to the next plan. If you are using the free version, the load caused by brute force attacks will be absorbed by your current hosting bandwidth, which could cause your hosting costs to increase.

What URLs are being attacked and protected?

The URLs being protected are your login page (wp-login.php, wp-admin), xmlrpc.php, WooCommerce login page, and any custom login page you have that uses regular WordPress login hooks.

Why is Limit Login Attempts Security more popular than other brute-force protection plugins?

Our main focus is protecting your site from brute force attacks. This allows our plugin to be very lean and effective. It doesn’t require a lot of your web hosting resources and keeps your site well-protected. More importantly, it does all of this automatically as our service learns on its own about each IP it encounters. In contrast, a firewall would require manual blocking of IPs.

What to do when an admin gets blocked?

Open the site from another IP. You can do this from your cell phone, or using Opera browser and enabling free VPN there. You can also try turning off your router for a few minutes and then see if you get a different IP address. These will work if your hosting server is configured correctly. If that doesn’t work, connect to the site using FTP or your hosting control panel file manager. Navigate to wp-content/plugins/ and rename the limit-login-attempts-reloaded folder. Log in to the site then rename that folder back and whitelist your IP. By upgrading to our premium app, you will have the unlocking functionality right from the cloud so you’ll never have to deal with this issue.

What settings should I use In the plugin?

The settings are explained within the plugin in great detail. If you are unsure, use the default settings as they are the recommended ones.

Can I share the safelist/denylist throughout all of my sites?

By default, you will need to copy and paste the lists to each site manually. For the premium service, sites are grouped within the same private cloud account. Each site within that group can be configured if it shares its lockouts and access lists with other group members. The setting is located in the plugin’s interface. The default options are recommended.

Ratings & Reviews

Recent Reviews

Loading reviews...

View all reviews on WordPress.org (opens in a new tab)

Changelog

3.3.7

  • Fixed PHP warnings when a cloud app custom setting is missing the label, description, or value field.
  • Added the SameSite=Lax attribute to the login flow cookie for better CSRF protection.
  • Fixed dashicons line-height on all admin pages and dashboard widgets for WordPress 7 compatibility.
  • Fixed the cloud app setup so it verifies the setup code was saved before activating the custom app, preventing an inconsistent state on storage errors.
  • Fixed the review admin notice buttons not working because its inline script was being stripped by output sanitization.
  • Fixed the Micro Cloud setup so it surfaces the actual server error message to admins and handles an incomplete app configuration gracefully instead of failing silently.

3.3.6

  • Refactored the core plugin class into smaller services.

3.3.5

  • Hardened denylist matching to make username blocking more reliable and consistent. Thanks to Artus KG for finding and reporting this issue.

3.3.4

  • Fixed icon positioning.

3.3.3

  • Fixed the dashboard incorrectly showing a network error when the cloud API is reachable but access is restricted.
  • Fixed a PHP 8.1+ deprecation notice by avoiding implicit float-to-int conversion in the lockout email notification check.
  • Made the email digest labels (Daily/Weekly/Monthly) and preview text translatable.
  • Allowed safelisted usernames (matched case-insensitively, including by email) to bypass lockouts and the MFA prompt on login.

3.3.2

  • Improved usage information in cloud mode.

Earlier versions

For the changelog of earlier versions, please refer to the changelog.txt file.

Alternatives to Limit Login Attempts Security

Other WordPress plugins serving a similar purpose, ranked by relevance and PF Score.

Platinum97.1
Wordfence Security – Firewall, Malware Scan, and Login Security icon

Wordfence Security

Firewall, malware scanner, and two-factor authentication for WordPress site security.

★ 4.7/5·5.0M+ installs·Updated 10 Aug 2026
Platinum90.6
Defender Security – Malware Scanner, Login Security & Firewall icon

Defender Security

Malware scanner, firewall, login security, and audit logs for WordPress site protection.

★ 4.8/5·80K+ installs·Updated 24 Aug 2026
Platinum89.3
WP Ghost (Hide My WP Ghost) – Security & Firewall icon

WP Ghost (Hide My WP Ghost)

Hides WordPress paths and applies firewall protection, brute force blocking, and passkey login security.

★ 4.5/5·100K+ installs·Updated 3 Sep 2026
Platinum87.9
Shield Security – Smart Bot Blocking, Brute-Force Login Protection & File Scanning icon

Shield Security

Blocks bots automatically and repairs security issues while filtering out non-critical alerts.

★ 4.8/5·30K+ installs·Updated 27 Aug 2026
Platinum86.4
BulletProof Security icon

BulletProof Security

Malware scanner and firewall with login security, database backup, and anti-spam features.

★ 4.8/5·20K+ installs·Updated 19 Aug 2026
Platinum99.1
Really Simple Security – Simple and Performant Security (formerly Really Simple SSL) icon

Really Simple Security

Hardens WordPress security with two-factor authentication, login protection, and vulnerability detection across 3 million active sites.

★ 4.9/5·3.0M+ installs·Updated 1 Sep 2026
Platinum90.9
NinjaFirewall (WP Edition) – Advanced Security Plugin and Firewall icon

NinjaFirewall (WP Edition)

Web application firewall designed to protect WordPress sites from malware and security threats.

★ 4.9/5·100K+ installs·Updated 16 Aug 2026
Platinum90.8
Sucuri Security – Auditing, Malware Scanner and Security Hardening icon

Sucuri Security

Provides malware detection, integrity monitoring, and security hardening for WordPress sites.

★ 4.2/5·600K+ installs·Updated 7 Jul 2026